MANDATE / ISO/IEC 27001:2022
A system of record for ISO/IEC 27001.
For small organisations going for certification without a compliance team. Mandate takes you from the decision to certify through to the surveillance audits, holds every register the standard asks for, and seals each approval as it's made.
EARLY ACCESS
THE FIRST CUSTOMER IS SETTING IT UP NOW
For the people who carry an ISO 27001 programme in a small firm: the person who's been handed the management system, the directors who have to lead it, the consultant setting it up, and the auditor who checks it.
01 / EVIDENCE
Every item of evidence says how it's known.
An approved policy shows a control was designed. Only a record that something was done shows it ran. Mandate keeps the two apart, doesn't count a draft or a plan as either, and lists by name the controls with nothing behind them.
02 / THE PATH
One path, from deciding to certify to the surveillance audits.
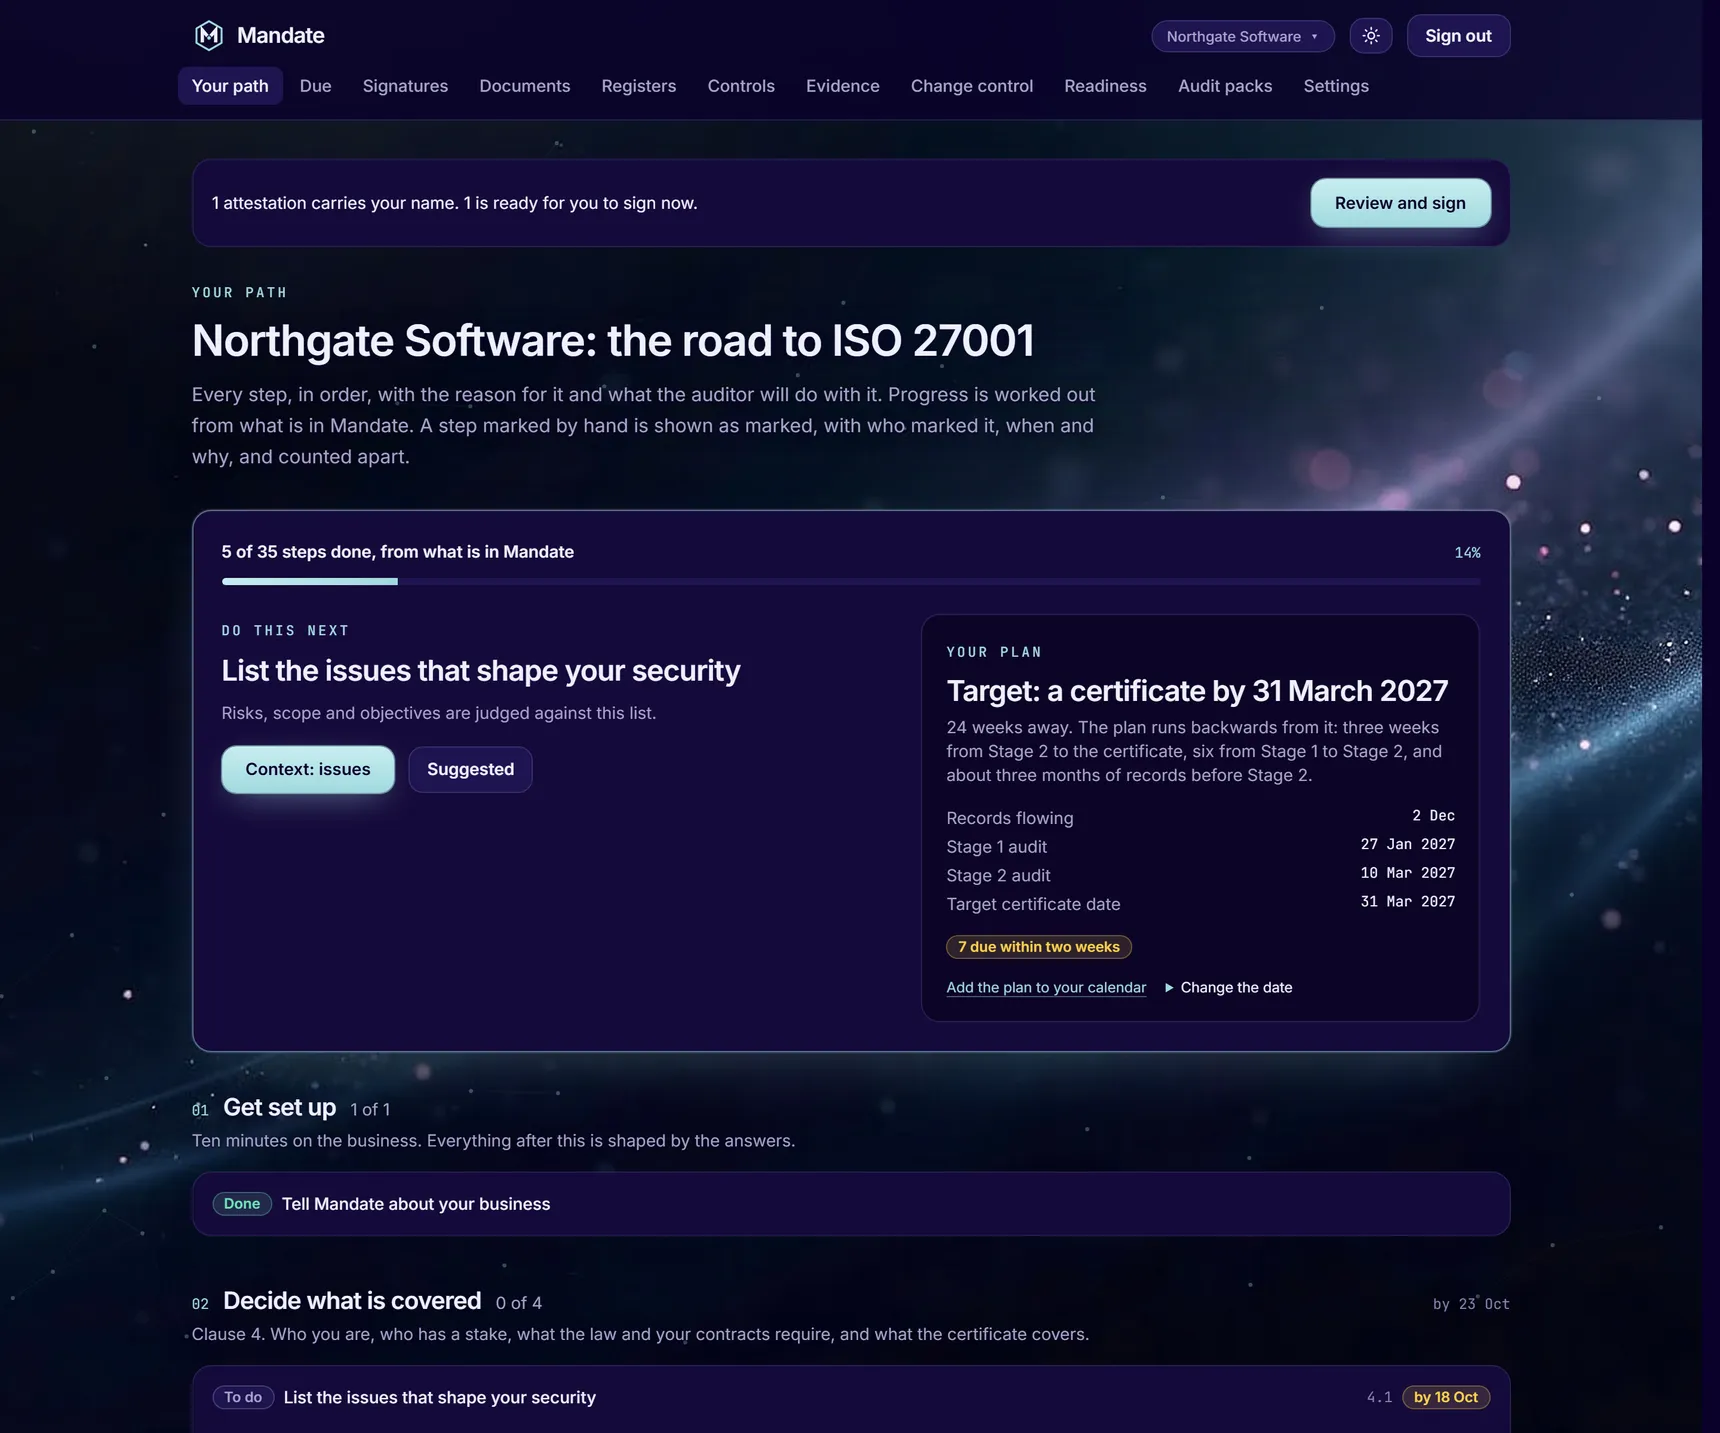
Each step says why it matters, what the auditor looks for and what done looks like. Progress is worked out from what you've entered. A step you mark by hand shows as marked, with who marked it and why.
- 01Decide
Scope, context, interested parties and how you'll judge risk, in plain questions.
- 02Build
Registers, policies and the Statement of Applicability, starting from the documents you have.
- 03Run
A calendar of control tasks. Each run is recorded and sealed when it's done.
- 04Prove
Readiness read strictly, then Stage 1 and Stage 2 packs for the auditor.
THE PRODUCT, IN USE
Real screens, from a fictional company working towards its certificate.
Each view is Mandate as Northgate Software sees it. Northgate is a demonstration organisation; nothing here is a client's.
SET UP
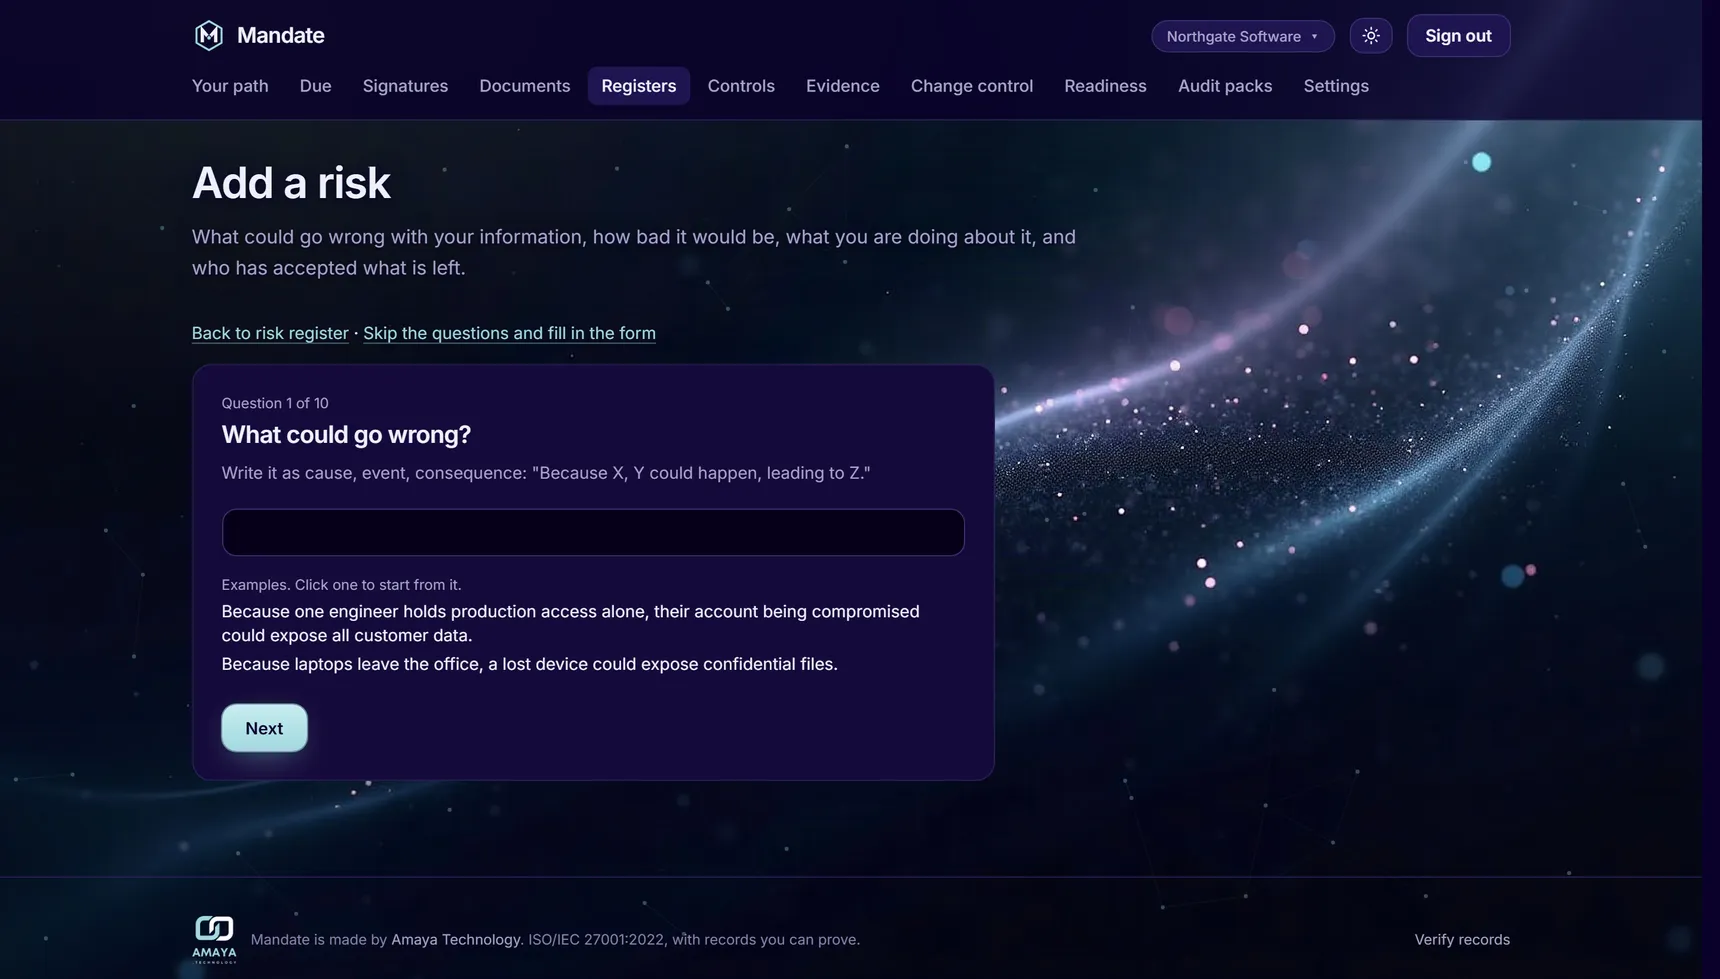
Answer plain questions. Keep the documents you already have.
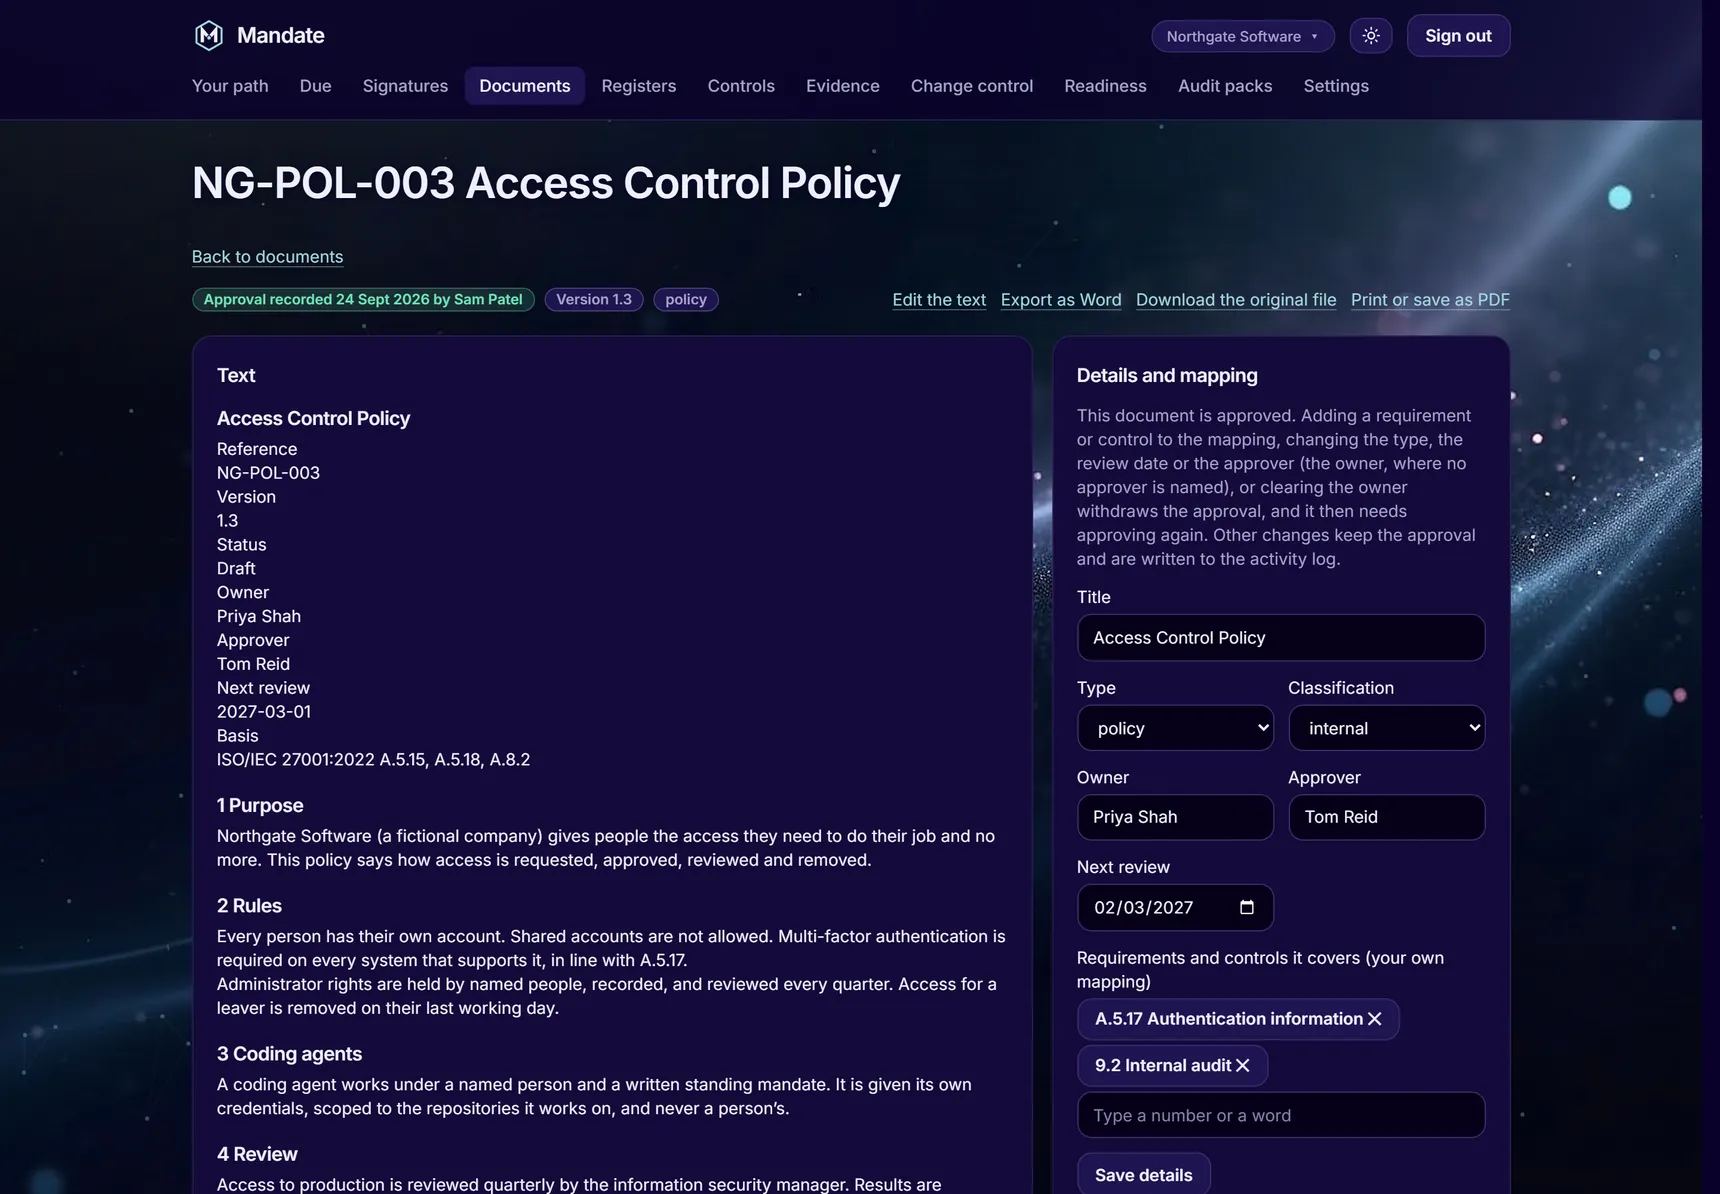
Every register has a guide that asks one question at a time, and a plain form. Your policies come in from Word, Excel or PDF, get mapped to the clauses and controls they cover, and stay drafts until the named approver approves them.
RUN
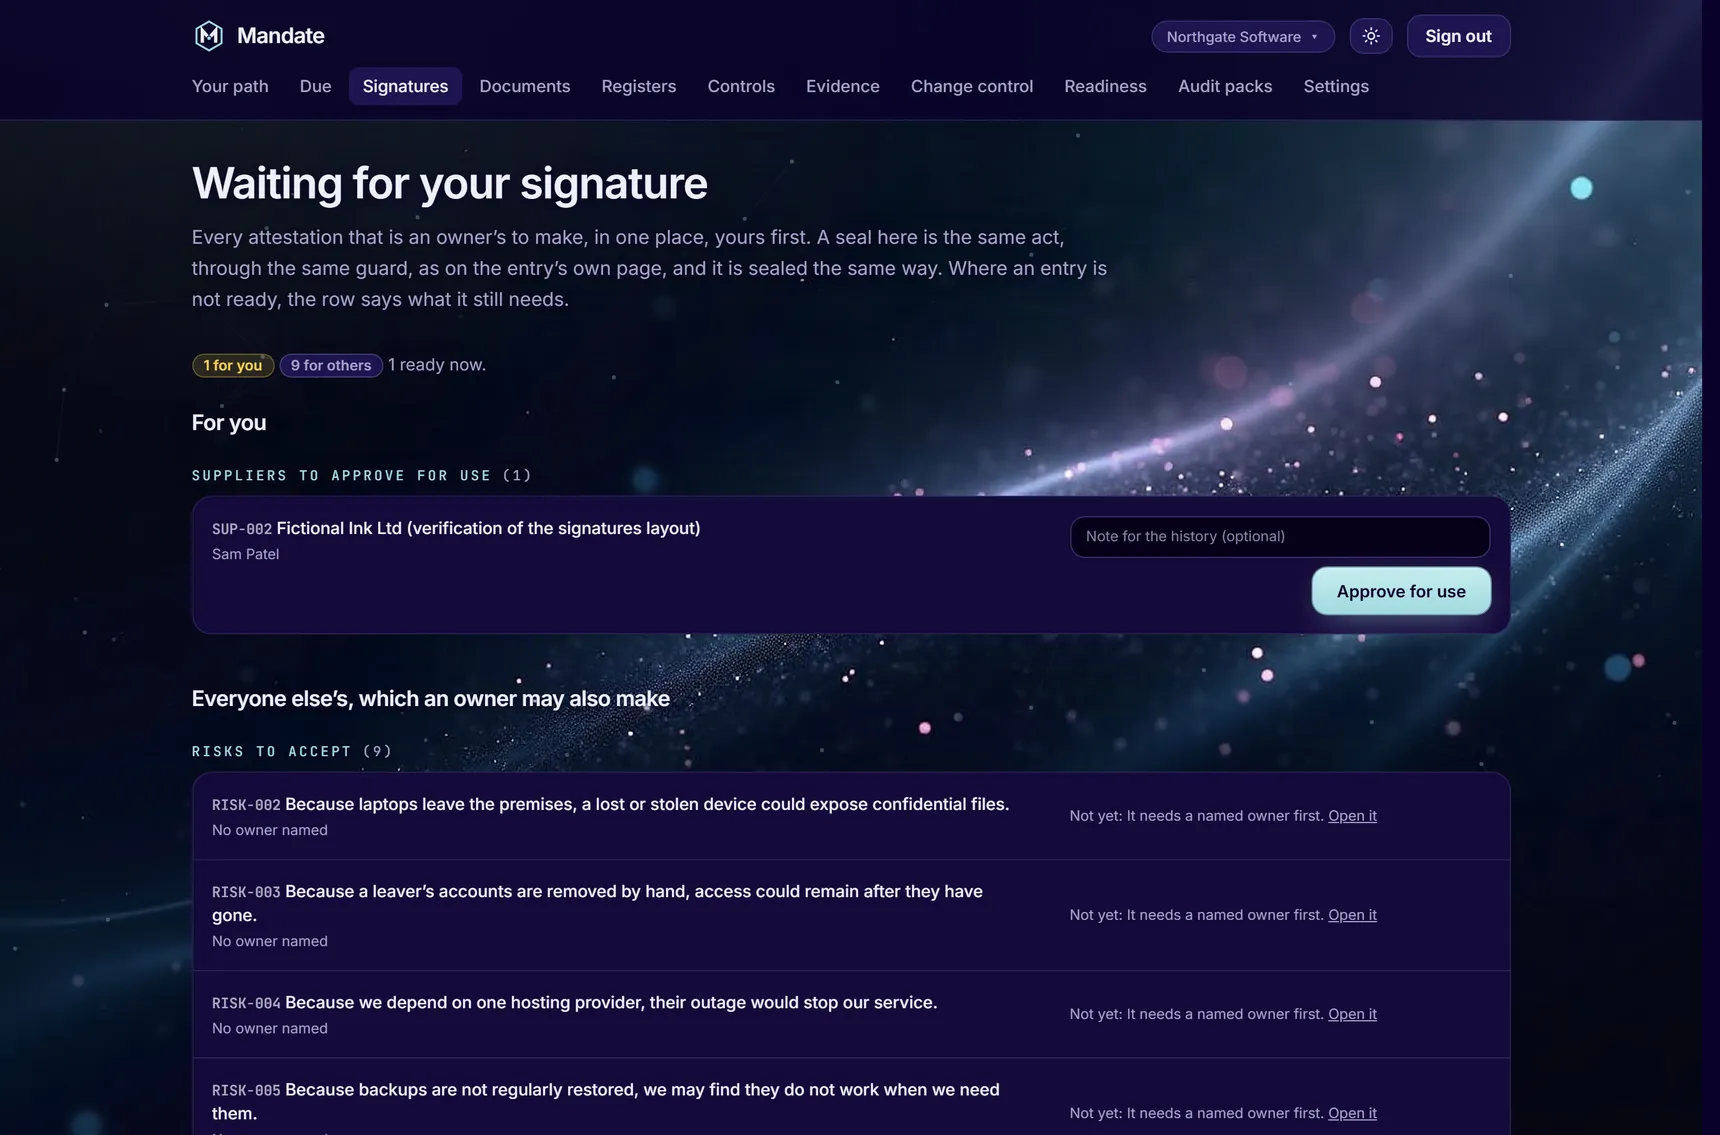
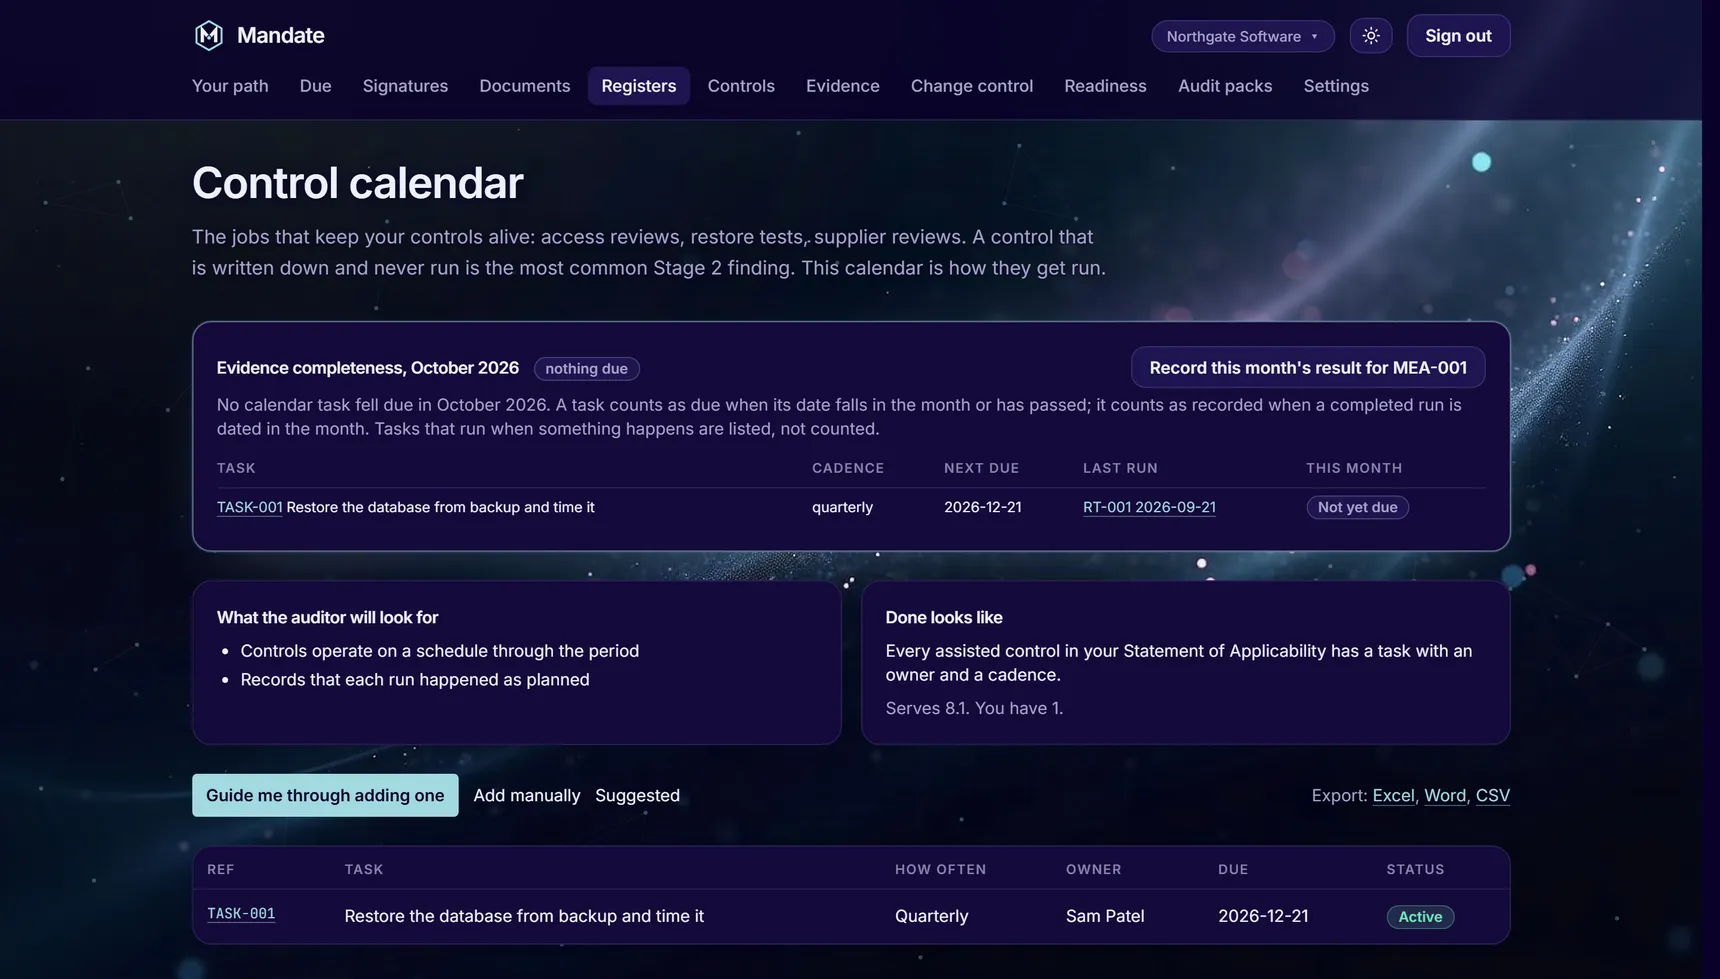
Know what's due, and who has to sign.
The calendar holds the jobs that keep controls running. Recording a run seals it and moves the next due date on. The attestations that are an owner's to make wait in one place, each saying what it still needs.
PROVE
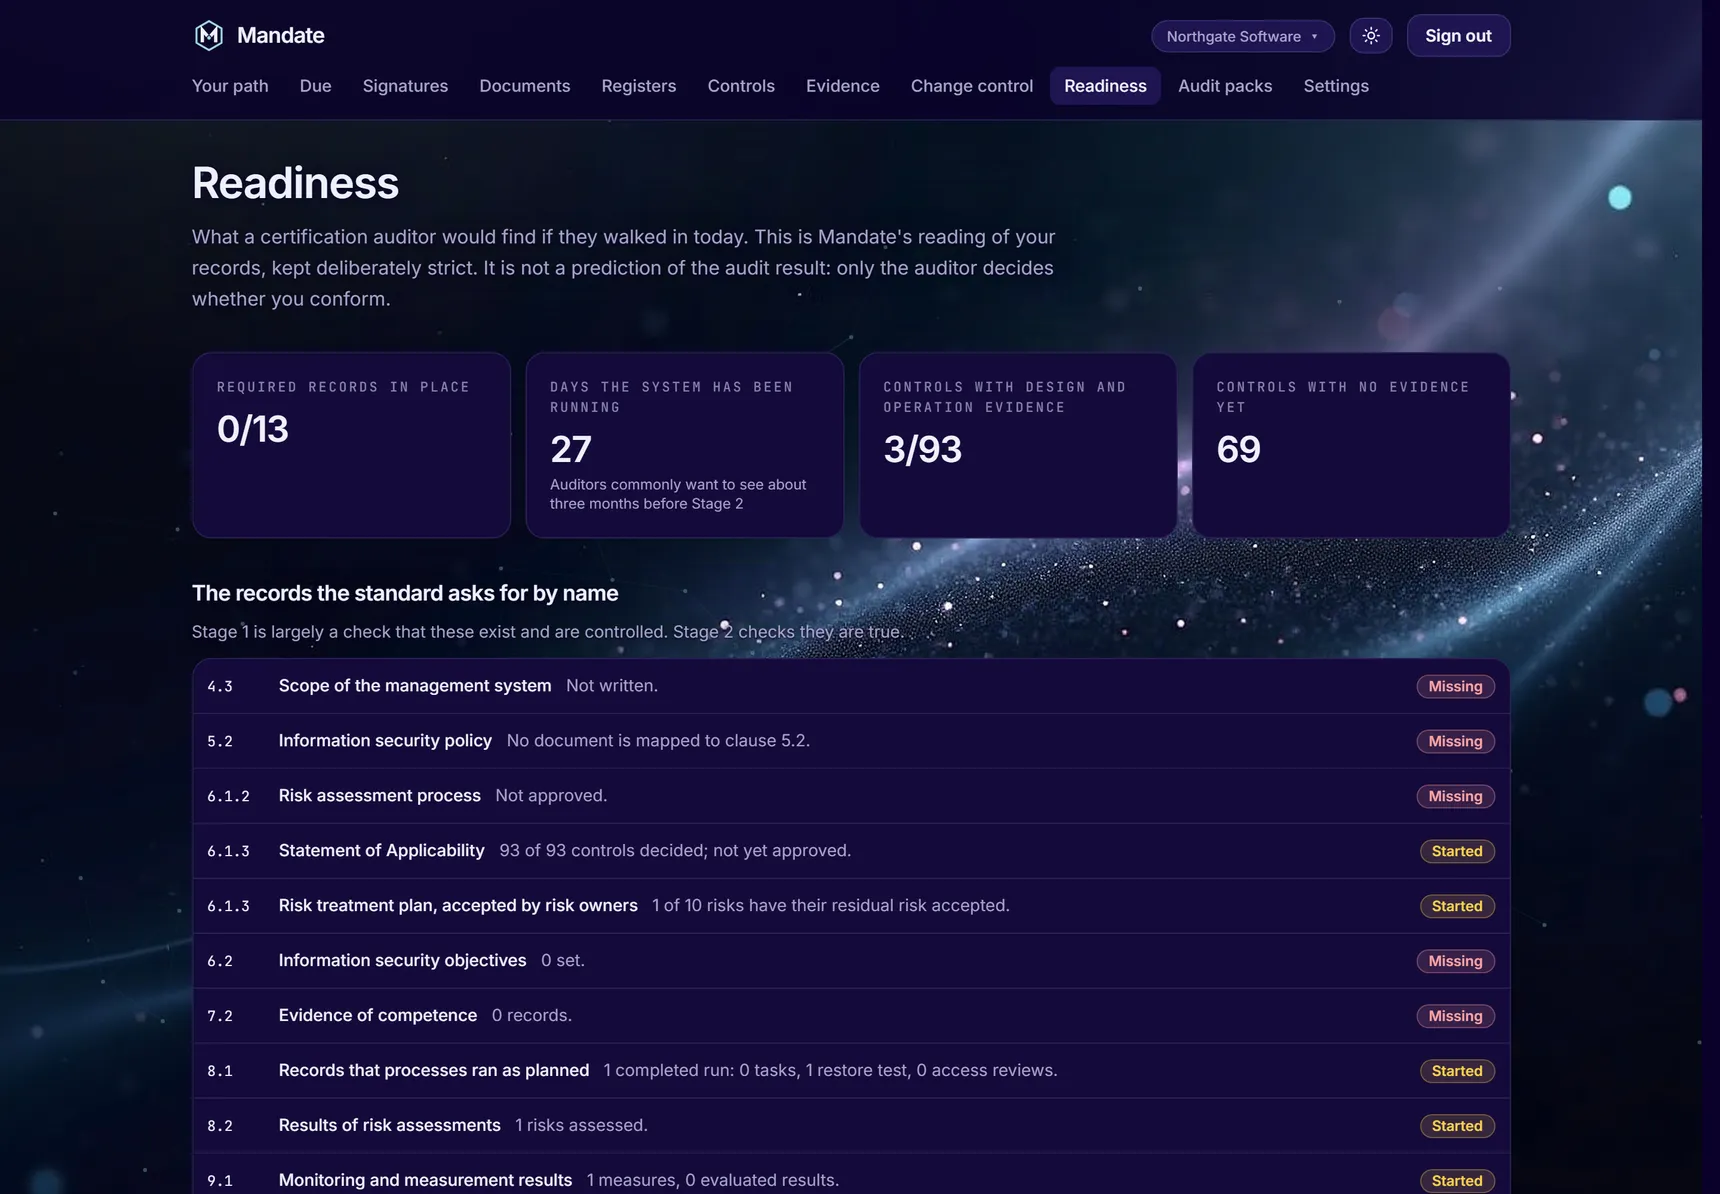
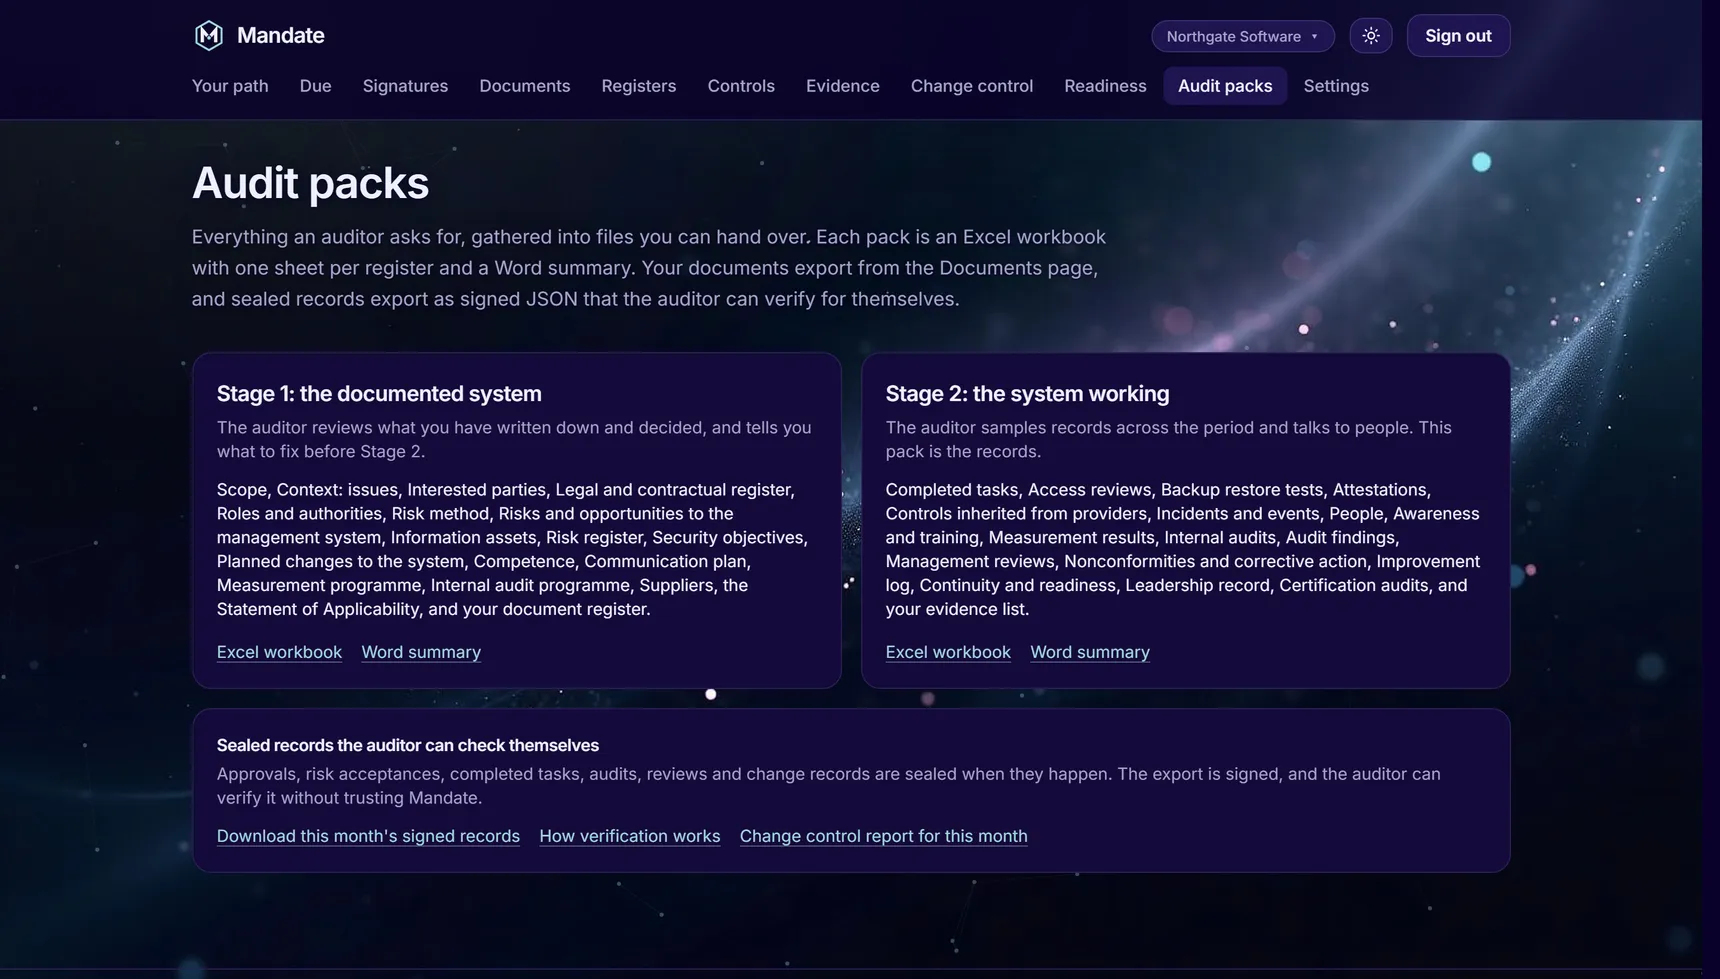
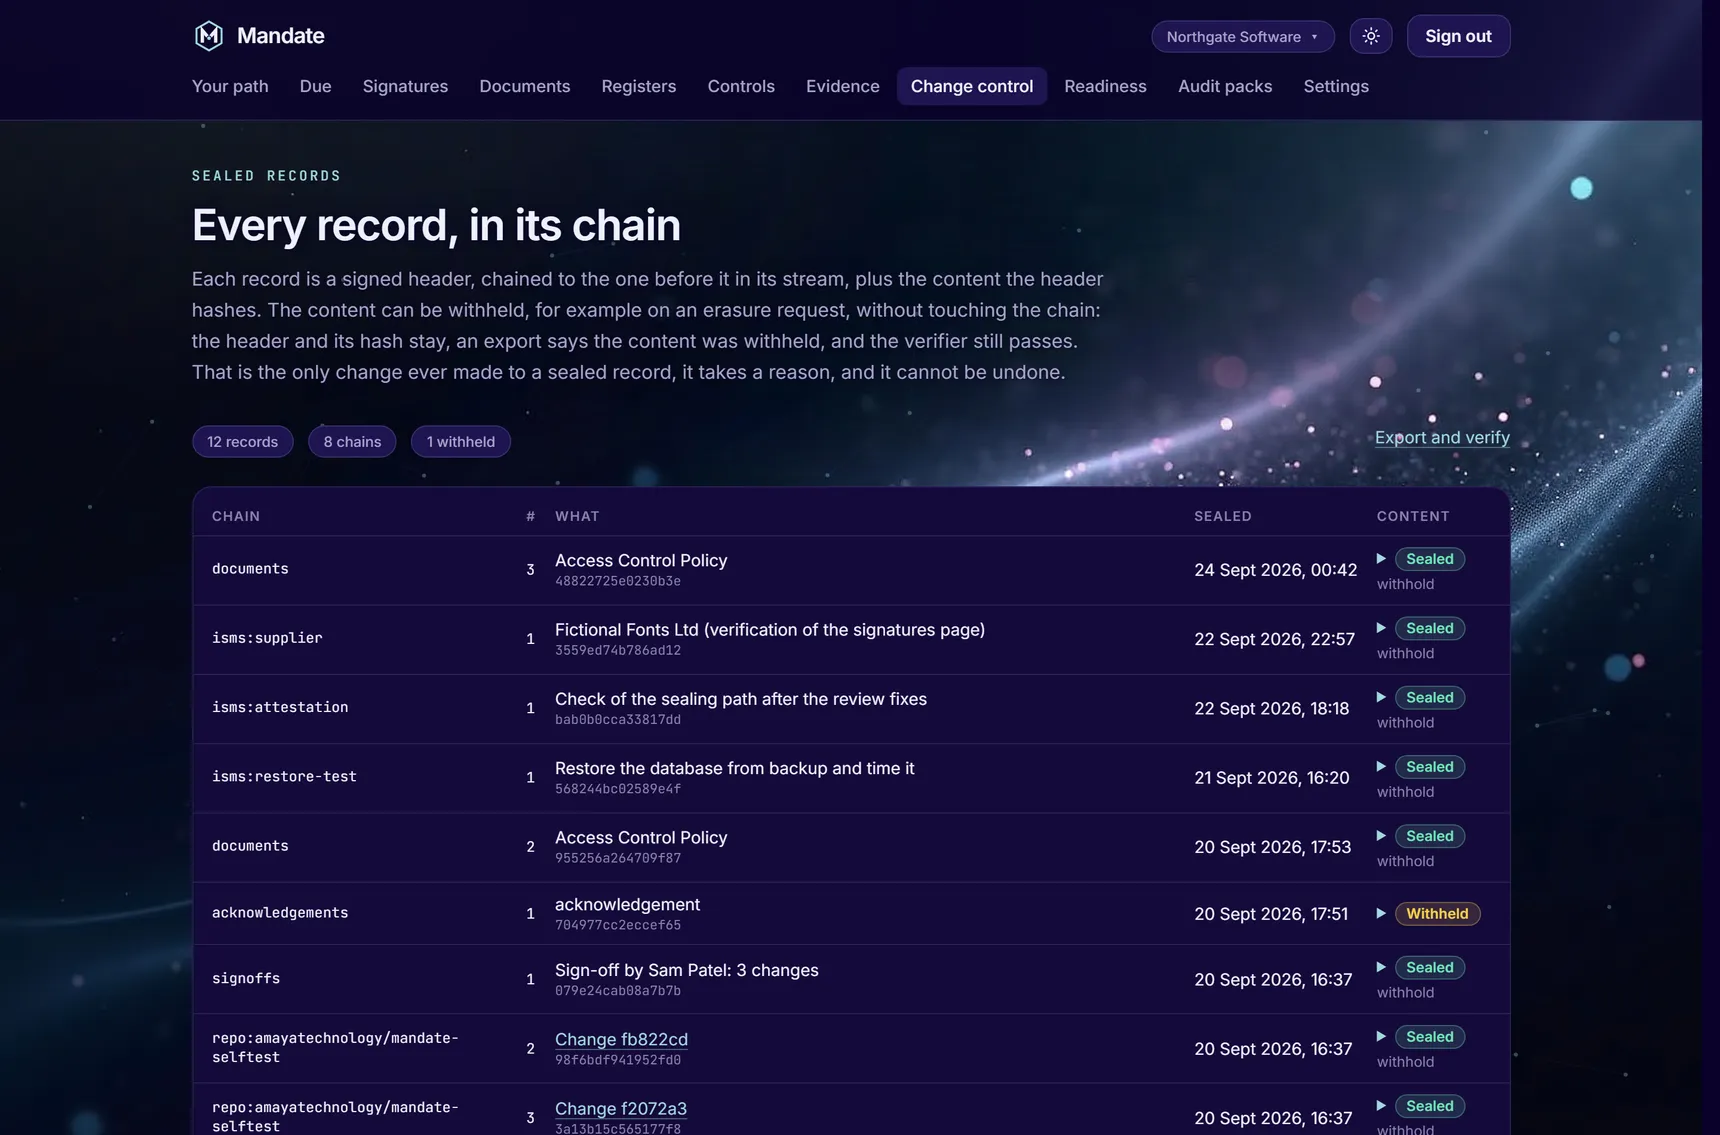
See what an auditor would find, then hand it over.
Readiness lists the records the standard asks for by name and says which are missing. The Stage 1 and Stage 2 packs gather the registers into files for the auditor, and sealed records export as signed JSON they can check themselves.
03 / CONTROLS
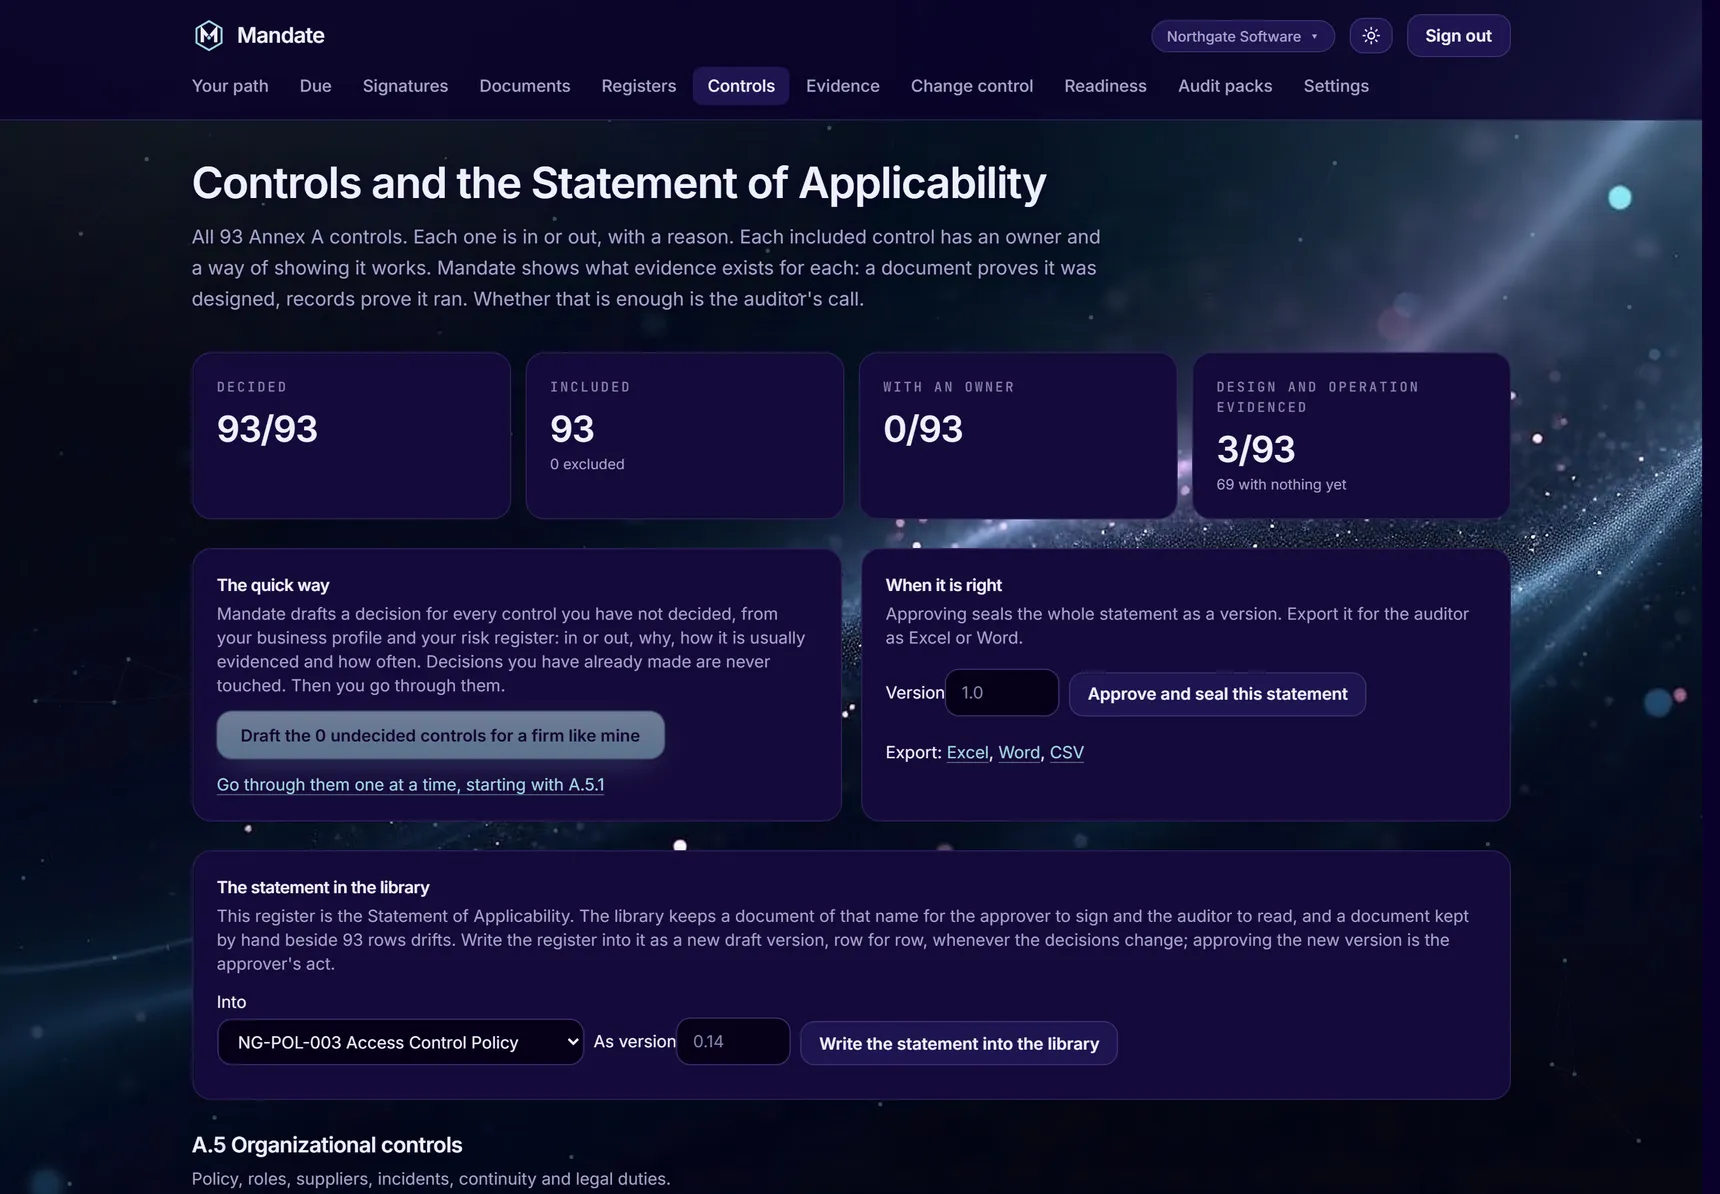
Every Annex A control has a decision, an owner and a way of showing it works.
The controls register is your Statement of Applicability. Mandate drafts a decision for each control from your set-up answers and your risks, and you go through them. The statement in your library is written from the register, not kept by hand beside it.
- In or out, with the reason, for all 93 controls
- Design evidence and operation evidence counted separately
- Approved and sealed as a version, exported to Excel or Word
04 / AI AGENTS
Code written by an AI agent still needs someone's authority.
Mandate records what coding agents such as Claude Code do in your repositories: the instruction, the tool calls, the commits, the checks and the deployment. Each change is judged against a mandate a person granted beforehand, then signed off and sealed. That's change management evidence (A.8.32) when an agent wrote the code.
How it handles AI agents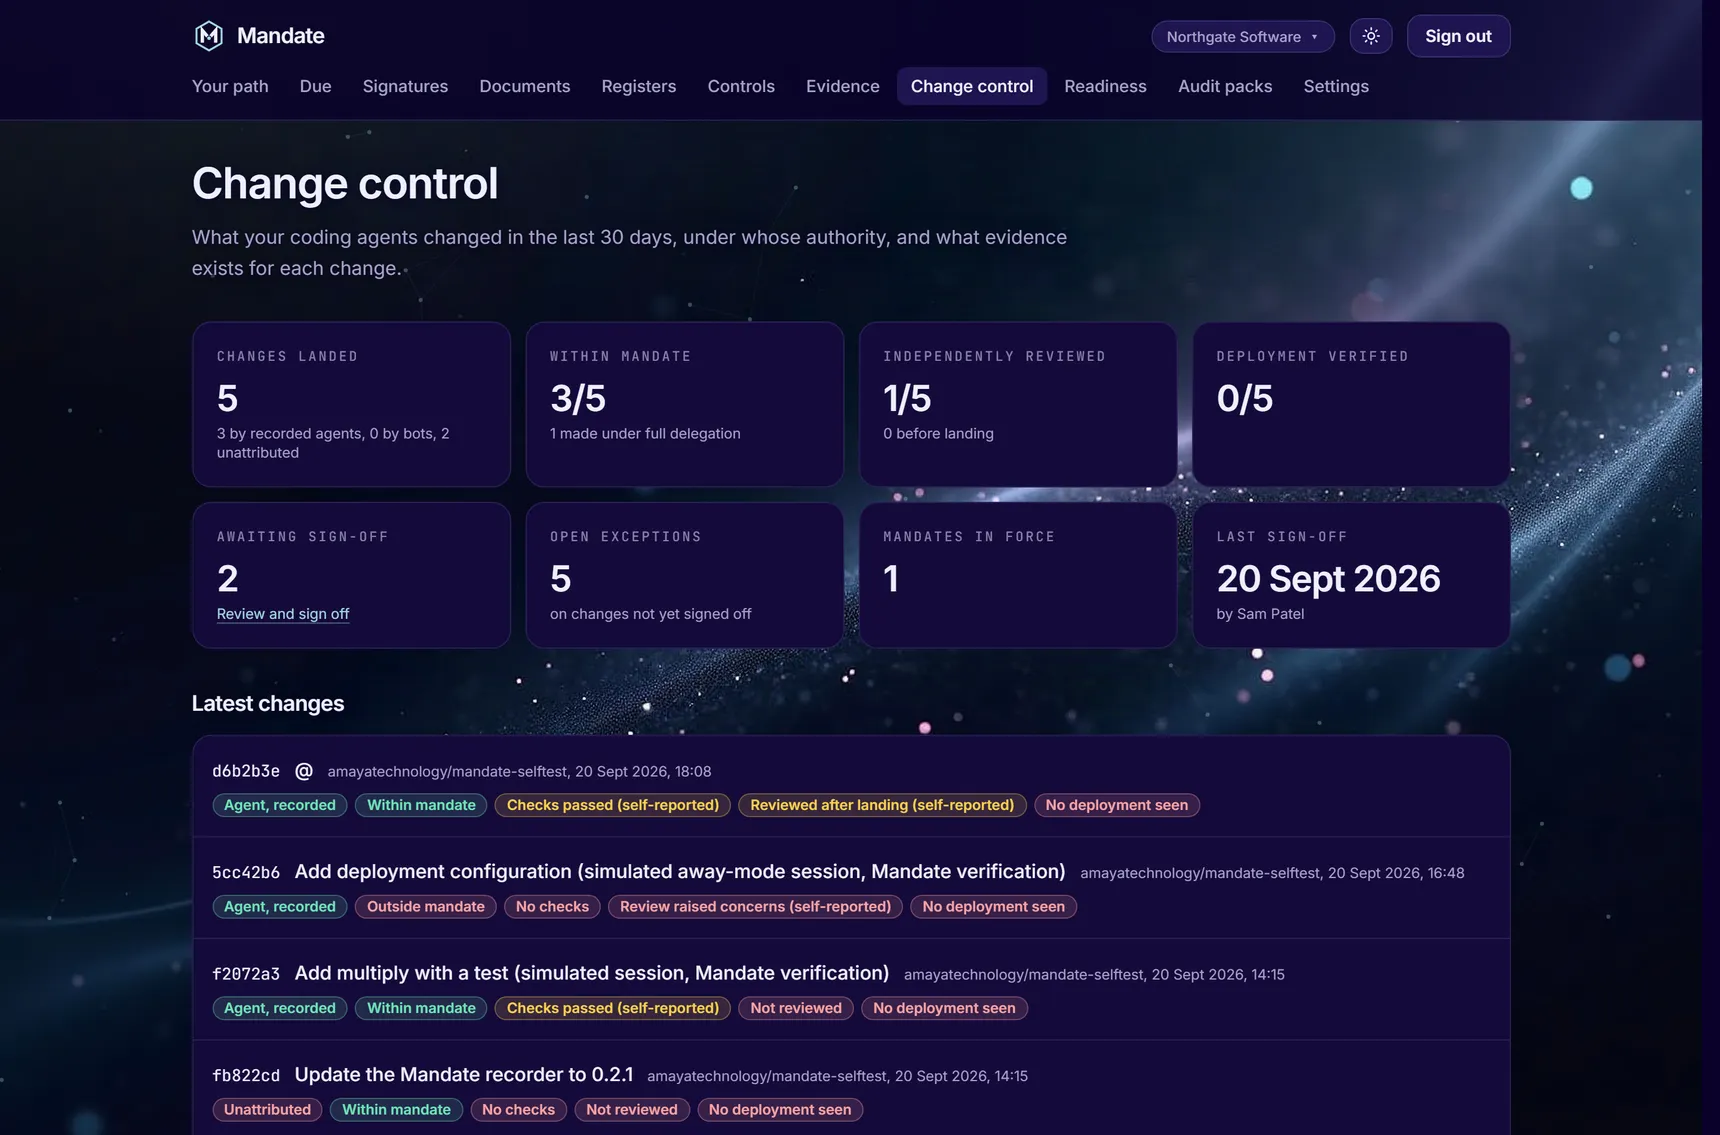
05 / THE AUDITOR
Give the auditor a link, not a shared drive.
The auditor gets one link that expires, with no account to set up. What they raise comes straight into your registers.
- Readiness, controls and documentsThe same strict reading you see, with each item's evidence and how it's known.
- A sample anyone can repeatThe seed is recorded, so the same draw comes out again.
- Requests and findingsRaised in the portal and created in your registers, marked as the auditor's.
- Withdrawn when you chooseThe link stops working as soon as you withdraw it, or when it expires.
06 / SEALED RECORDS
Sealed when they're made, and you can check them yourself.
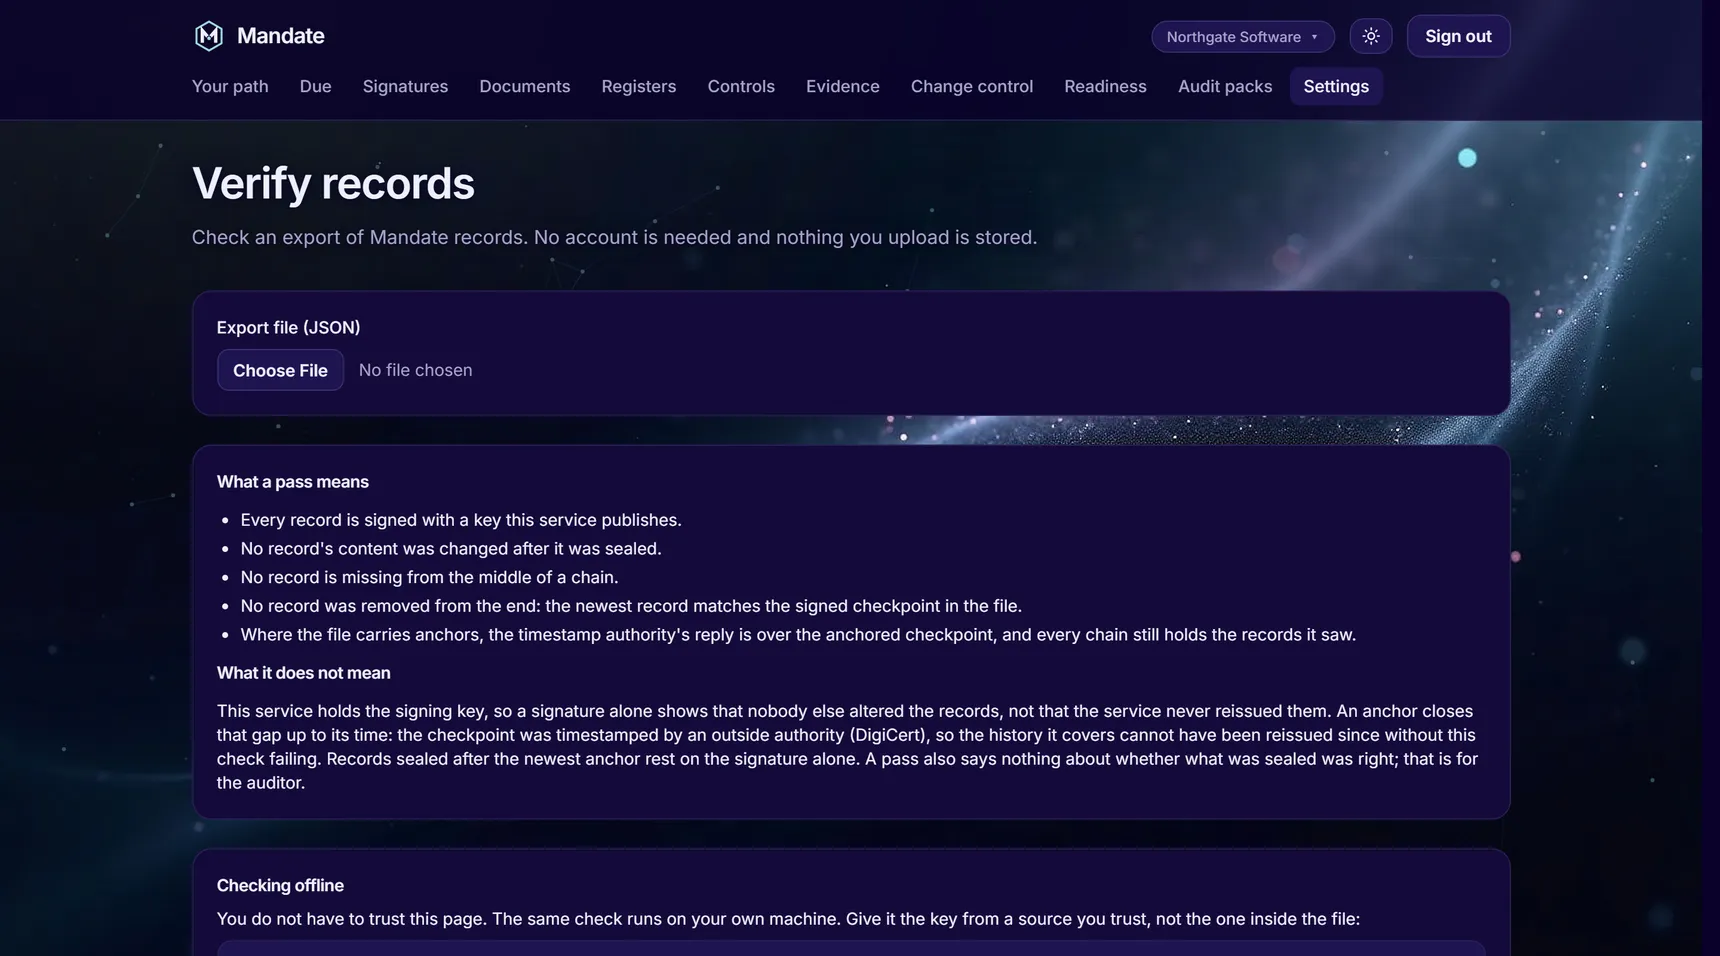
Approvals, attestations, completed tasks and change records are signed and chained to the record before them. Exports and sign-offs are timestamped by an independent authority. Anyone can check an export offline with the published key, and a record changed after it was sealed fails.
SEE IT ON A WORKING EXAMPLE
Find out where your ISO 27001 programme stands before the auditor does.
We'll walk the path with you on our demonstration organisation and show you where your own documents and records would go.
Request a walkthrough